The threat landscape has never been noisier. Every week produces new advisories, new attack reports, new vulnerability disclosures, and new frameworks for thinking about risk. For regulated organisations, the noise carries an additional dimension: the expectation from supervisors that the organisation is paying attention and can demonstrate it.
The response, in many cases, is to pay attention to everything. That isn’t a strategy. It’s a posture, and it produces anxiety, misallocated attention, and a security function that is reactive by design.
What the noise actually contains
Threat intelligence reporting is not uniform in relevance or quality. The majority of what is published describes threats that are real in the aggregate but not material to any specific organisation’s context.
Nation-state activity against critical national infrastructure is significant. It is not equally significant for a mid-sized financial institution, a regional healthcare provider, and a multinational energy company. Ransomware campaigns targeting healthcare are relevant to healthcare organisations. They are background noise for most others.
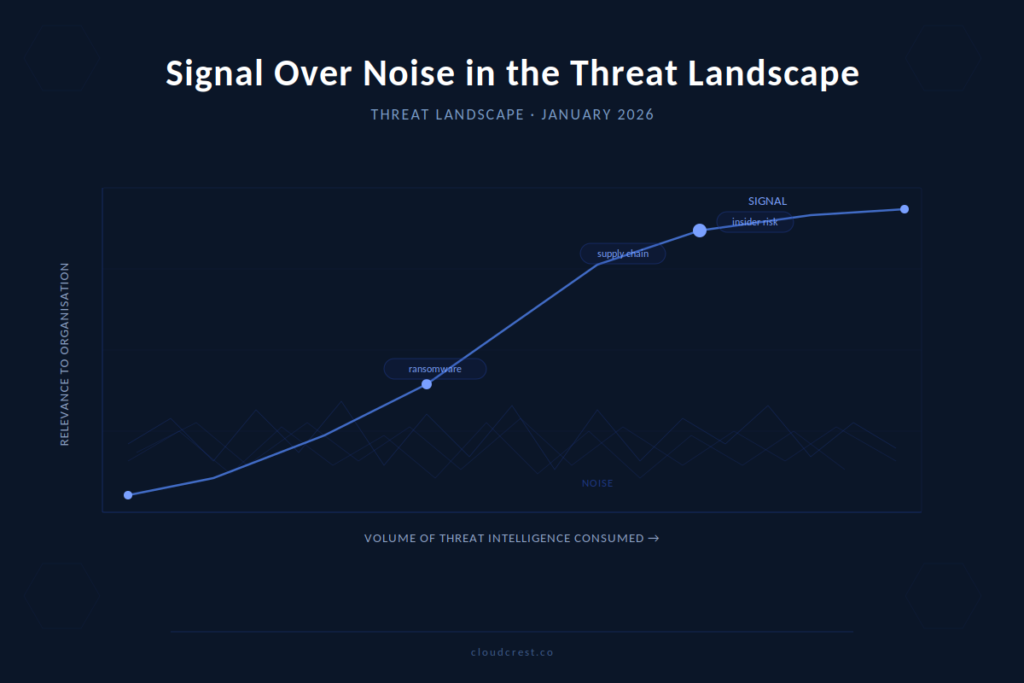
What’s required here is tighter filtering, not broader coverage. Organisations that consume threat intelligence well have a clear view of their threat actor profile, their most significant attack surfaces, and the plausible scenarios they are actually exposed to. They use intelligence to validate or challenge that view rather than expand it without limit.
The regulatory dimension
Regulated organisations face a particular pressure that can distort threat landscape analysis. Regulators expect evidence of awareness. This expectation sometimes translates internally into a requirement to be seen tracking everything, which confuses coverage with comprehension.
What regulators actually want to understand is whether the organisation has a coherent view of the threats it faces and whether its controls are calibrated to that view. Subscribing to seventeen threat feeds and producing a weekly briefing for the risk committee doesn’t satisfy this. Understanding why ransomware is your most plausible high-impact scenario, and showing how your controls address it, does.
The difference is between intelligence consumption and intelligence application. Regulators are increasingly sophisticated about this distinction. Volume of reporting is no substitute for quality of analysis.
Where attention should actually go
For most regulated organisations, the threat landscape that actually matters is narrower than the one being monitored.
Financially motivated attacks — ransomware, business email compromise, account takeover — remain the dominant operational risk for the vast majority of regulated entities. The mechanics keep evolving, but the underlying pattern holds steady. Controls designed around this reality are more valuable than those designed to address the full breadth of what the threat landscape nominally contains.
Supply chain and third-party risk represents the fastest-growing area of genuine exposure. Regulatory frameworks have caught up with this. For most organisations the real question is whether their current third-party oversight is adequate to the actual concentration of risk in their supplier base.
Insider risk is consistently underweighted. It is less visible, less dramatic, and less amenable to technology-led solutions than external threat categories. It also produces some of the most damaging outcomes. Regulated organisations that have invested heavily in perimeter and detection capabilities without commensurate investment in insider risk management have a structural gap.
Judgment matters more than coverage
The value a security function provides to an organisation isn’t measured by the breadth of the threat intelligence it consumes. It’s measured by the quality of the judgments it makes about what matters, and by how well those judgments translate into proportionate controls and defensible decisions.
Regulators aren’t looking for organisations that have read everything. They’re looking for organisations that understand their own risk position and can articulate it clearly. The threat landscape is a source of information for that exercise, nothing more.
Organisations that mistake consumption for comprehension tend to be busy, reactive, and perpetually behind. The ones that filter deliberately and apply judgment consistently engage better with regulators and hold up better against adversaries.