The EU AI Act is now in force. Most organisations subject to it are not ready. That gap is a governance problem, and the compliance machinery organisations have applied to every regulation before this one won’t resolve it.
AI regulation is different in kind from what most compliance functions have encountered. The obligations it creates do not map cleanly onto controls that can be documented, audited, and signed off. They require ongoing human judgment about systems that behave probabilistically, that change over time, and that produce outputs that cannot always be predicted or explained. Treating this as a standard compliance exercise produces an illusion of readiness that regulators will not find convincing.
What the Act actually demands
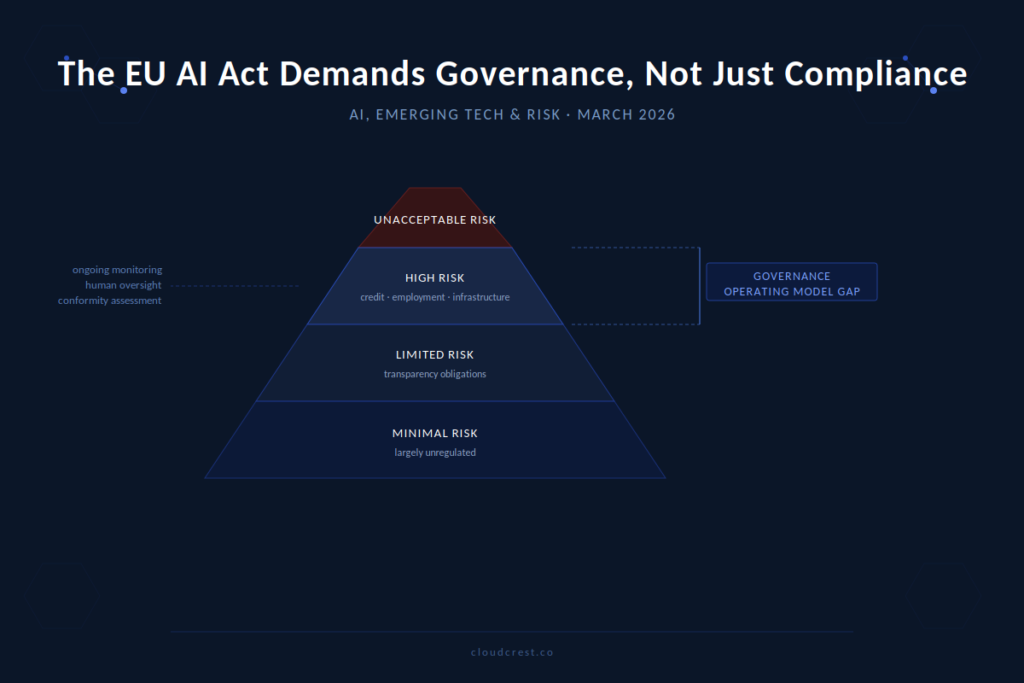
The EU AI Act establishes a risk-tiered framework. High-risk AI systems are those used in credit decisioning, employment screening, critical infrastructure management, and a range of other regulated contexts. They carry significant obligations around transparency, human oversight, data governance, and ongoing monitoring.
The obligations themselves are straightforward. What’s hard is that they require institutional accountability structures most organisations have not built. Who owns the decision to deploy a high-risk AI system? Who is responsible for monitoring its performance against the criteria that justified its approval? Who has the authority to suspend it when performance degrades or context changes?
These are governance questions. The AI Act does not answer them. It requires organisations to answer them, and to show the answers hold up in practice.
Why existing compliance models fail here
The compliance approach most organisations will reach for first is documentation. Map the AI systems in use. Classify them by risk tier. Produce conformity assessments for those in scope. File the paperwork. Repeat at the next review cycle.
This model has a structural flaw when applied to AI. AI systems are not static. A model trained on data from one period behaves differently when the underlying distribution shifts. A system that performed within acceptable parameters at deployment may drift outside them without any change to the system itself. Documentation that was accurate at the time of conformity assessment may be misleading six months later.
The Act anticipates this. Its post-market monitoring and logging requirements reflect a regulatory view: AI compliance is an ongoing operating condition. Organisations that treat it as a one-time certification end up technically compliant and practically exposed.
The governance operating model that is missing
Most organisations already know about the AI Act. What they lack is a governance operating model that makes compliance sustainable.
A governance operating model for AI requires, at minimum, clear ownership of each high-risk system, held by one named individual. It requires decision rights that are explicit about who can approve deployment, who can escalate concerns, and who has authority to withdraw a system from use. It requires a monitoring cadence proportionate to the risk the system carries and the rate at which its operating context changes.
It also requires that the organisation has resolved a foundational question that many have not: what does human oversight actually mean for their AI deployments? The Act requires meaningful human oversight of high-risk systems. The word “meaningful” is doing a lot of work in that sentence. An override button that nobody exercises, or a review process that rubber-stamps model outputs, does not satisfy the intent. Regulators will probe this directly.
The implications for decision-makers
Boards and executive teams that treat AI Act compliance as a project to be delivered by the legal or compliance function are setting themselves up for a difficult regulatory conversation.
The obligations the Act creates sit at the intersection of technology, operations, and governance in a way that no single function can own. The compliance function can map requirements. It cannot, on its own, build the accountability structures, the monitoring infrastructure, or the decision-making processes that genuine compliance requires.
Organisations that navigate this well recognise AI governance as a cross-functional operating discipline. They invest in the institutional capacity to make and record decisions about AI systems on an ongoing basis, well beyond the point of deployment.
The EU AI Act will expose a divide between organisations that have built this capacity and those that have produced documentation in its place. That divide will be visible to regulators, and increasingly to the organisations themselves, well before any formal enforcement action arrives.